

Free Sales Ending Soon - Use Real SC-900 PDF Questions [May 10, 2026]
Updated May-2026 Exam SC-900 Dumps - Pass Your Certification Exam
NEW QUESTION # 83
What are two capabilities of Microsoft Defender for Endpoint? Each correct selection presents a complete solution.
NOTE: Each correct selection is worth one point.
- A. transport encryption
- B. automated investigation and remediation
- C. shadow IT detection
- D. attack surface reduction
Answer: B,D
Explanation:
Microsoft Defender for Endpoint includes Automated investigation and remediation (AIR) and Attack surface reduction (ASR) as core capabilities. Microsoft's guidance states that AIR "uses inspection algorithms and playbooks to examine alerts, determine if they are malicious, and then take remediation actions such as stopping processes, quarantining files, and rolling back changes." It is designed to "reduce the volume of alerts that require analyst attention and to remediate threats at machine speed across your estate," helping security teams contain and fix issues without manual intervention.
Defender for Endpoint also provides attack surface reduction features to proactively limit exposure. The Microsoft learn materials describe that ASR "helps organizations minimize areas that attackers can exploit," and includes "attack surface reduction rules, network protection, web protection, application control (Windows Defender Application Control), and controlled folder access." These controls "block or constrain risky behaviors and common attacker techniques," thereby preventing many initial compromise and lateral- movement attempts before they generate incidents.
By contrast, transport encryption is a general platform/security baseline capability rather than a specific Defender for Endpoint feature, and shadow IT detection is addressed through Microsoft Defender for Cloud Apps (App discovery), which can use Defender for Endpoint network signals but is not itself a native MDE capability. Therefore, the two correct capabilities of Microsoft Defender for Endpoint are Automated investigation and remediation and Attack surface reduction.
NEW QUESTION # 84
Select the answer that correctly completes the sentence.
Answer:
Explanation:
NEW QUESTION # 85
Select the answer that correctly completes the sentence.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/security/fundamentals/customer-lockbox-overview
NEW QUESTION # 86
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/identity-protection/overview-identity-protection https://docs.microsoft.com/en-us/azure/active-directory/identity-protection/concept-identity-protection-risks https://docs.microsoft.com/en-us/azure/active-directory/authentication/tutorial-risk-based-sspr-mfa
NEW QUESTION # 87
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/security/zero-trust/
NEW QUESTION # 88
Select the answer that correctly completes the sentence.
Answer:
Explanation:

NEW QUESTION # 89
Select the answer that correctly completes the sentence.
Answer:
Explanation:

NEW QUESTION # 90
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/security-center/azure-defender
https://docs.microsoft.com/en-us/azure/security-center/defender-for-storage-introduction https://docs.microsoft.com/en-us/azure/security-center/security-center-introduction
NEW QUESTION # 91
Which three tasks can be performed by using Azure Active Directory (Azure AD) Identity Protection? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
- A. Automate the detection and remediation of identity based-risks.
- B. Investigate risks that relate to user authentication.
- C. Create and automatically assign sensitivity labels to data.
- D. Configure external access for partner organizations.
- E. Export risk detection to third-party utilities.
Answer: A,B,E
NEW QUESTION # 92
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Graphical user interface, text, application, email Description automatically generated
Box 1: No
Compliance Manager tracks Microsoft managed controls, customer-managed controls, and shared controls.
Box 2: Yes
Box 3: Yes
NEW QUESTION # 93
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/conditional-access/overview
NEW QUESTION # 94
Which Microsoft portal provides information about how Microsoft cloud services comply with regulatory standard, such as International Organization for Standardization (ISO)?
- A. Azure Cost Management + Billing
- B. the Microsoft Endpoint Manager admin center
- C. the Azure Active Directory admin center
- D. Microsoft Service Trust Portal
Answer: D
Explanation:
The Microsoft Service Trust Portal contains details about Microsoft's implementation of controls and processes that protect our cloud services and the customer data therein.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/get-started-with-service-trust-portal?view=o365- worldwide
NEW QUESTION # 95
Select the answer that correctly completes the sentence.
Answer:
Explanation:
NEW QUESTION # 96
Select the answer that correctly completes the sentence.
Answer:
Explanation:
Explanation:
Multi-factor authentication is a process where a user is prompted during the sign-in process for an additional form of identification, such as to enter a code on their cellphone or to provide a fingerprint scan.
NEW QUESTION # 97
Microsoft 365 Endpoint data loss prevention (Endpoint DLP) can be used on which operating systems?
- A. Windows 10 and newer and macOS only
- B. Windows 10 and newer only
- C. Windows 10 and newer, Android, and macOS
- D. Windows 10 and newer and Android only
Answer: B
NEW QUESTION # 98
Select the answer that correctly completes the sentence.
Answer:
Explanation:
Explanation:
In Microsoft Sentinel, automation is delivered through playbooks, which are built on Azure Logic Apps.
Microsoft's Sentinel documentation explains that playbooks "help automate and orchestrate your response to threats" and can be triggered by analytics alerts or incidents to run predefined actions. Typical automated tasks include "enriching alerts with data, blocking IP addresses, disabling users, or creating tickets," allowing security teams to standardize and speed up their response and remediation processes. Sentinel also uses automation rules to decide when a playbook should run (for example, on incident creation or update), enabling consistent handling of common SOC tasks.
By contrast, the other options are not intended for automation: deep investigation tools are used to investigate incidents and entities; hunting search-and-query tools (built on KQL) are for proactive threat hunting rather than automating responses; and workbooks provide dashboards and visualizations for monitoring and reporting. Therefore, when the requirement is to automate common tasks-such as triggering actions across Microsoft 365 Defender, Azure, or third-party systems-the correct Sentinel capability is playbooks powered by Logic Apps. This aligns with the SCI guidance that emphasizes using Sentinel playbooks to "automate common workflows and response actions" and reduce manual effort while improving consistency and speed in security operations.
NEW QUESTION # 99
Which Azure Active Directory (Azure AD) feature can you use to provide just-in-time (JIT) access to manage Azure resources?
- A. Azure AD Privileged Identity Management (PIM)
- B. conditional access policies
- C. Azure AD Identity Protection
- D. authentication method policies
Answer: A
Explanation:
Azure AD Privileged Identity Management (PIM) provides just-in-time privileged access to Azure AD and Azure resources
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/privileged-identity-management/pim-configure
NEW QUESTION # 100
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 101
Select the answer that correctly completes the sentence.
Answer:
Explanation:
NEW QUESTION # 102
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/roles/concept-understand-roles https://docs.microsoft.com/en-us/azure/active-directory/roles/permissions-reference
NEW QUESTION # 103
Which feature provides the extended detection and response (XDR) capability of Azure Sentinel?
- A. support for threat hunting
- B. integration with Microsoft 365 Defender
- C. support for Azure Monitor Workbooks
- D. integration with the Microsoft 365 compliance center
Answer: B
NEW QUESTION # 104
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point
Answer:
Explanation:
Explanation:
Microsoft Defender for Cloud can detect vulnerabilities and threats for Azure Storage. Yes Cloud Security Posture Management (CSPM) is available for all Azure subscriptions. Yes Microsoft Defender for Cloud can evaluate the security of workloads deployed to Azure or on-premises. Yes Microsoft Defender for Cloud provides both workload protection and posture management. For Azure Storage, the Defender plan (Microsoft Defender for Storage) offers threat detection such as anomalous access, malware scanning, and sensitive-data threat alerts, while the CSPM guidance in Defender for Cloud flags misconfigurations that create vulnerabilities (for example, public blob access, weak TLS settings). CSPM capabilities-secure score, recommendations, and baseline assessments-are available to all Azure subscriptions (foundational CSPM), giving every tenant visibility into security posture without requiring a premium add-on for basic posture features. Beyond Azure, Defender for Cloud supports hybrid and multicloud: using Azure Arc and the Defender for Servers plan, it can onboard and assess on-premises servers and resources in other clouds, applying recommendations, security assessments, and threat protections across those environments. Collectively, these capabilities confirm that Defender for Cloud can detect storage- related threats and posture weaknesses, CSPM is broadly available to Azure subscriptions, and the service evaluates workloads running in Azure or on-premises.
NEW QUESTION # 105
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Graphical user interface, text, application, email Description automatically generated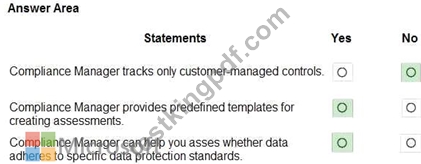
Box 1: No
Compliance Manager tracks Microsoft managed controls, customer-managed controls, and shared controls.
Box 2: Yes
Box 3: Yes
NEW QUESTION # 106
......
Get to know about the importance of Microsoft SC-900 Certification
Microsoft SC-900 certification is of core importance both to IT professionals and employers alike. Microsoft SC-900 exam deals with an advanced level of expertise therefore most people shy away from it. This professional level exam is targeted to provide technical assistance, data security, and at the same time reduce employee operating costs in an organization. It also helps in achieving a competitive advantage for the employees of the organization. Because of all these factors and more, the Microsoft SC-900 exam has become a hot cake among organizations and the people employed in them. Microsoft SC-900 Dumps are the best preparation tool for candidates who want to take the Microsoft SC-900 exam. It will help you get the required score quickly.
SC-900 Dumps To Pass Microsoft Certified Exam in One Day: https://examtorrent.testkingpdf.com/SC-900-testking-pdf-torrent.html
